Writeup Archive
Every challenge writeup from TryN3rr0r events. Filter by event or category, or search across titles and summaries.
GGEZAF
Dockerized box solved by chaining three misconfigurations
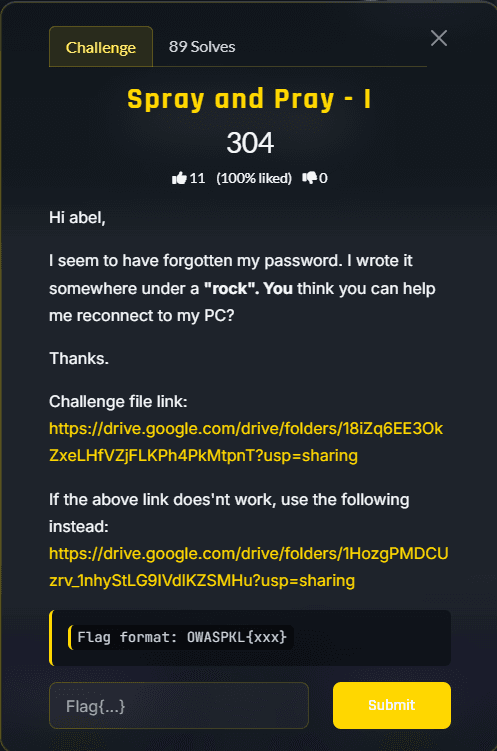
Spray and Pray - I
Target exposed only SSH. The challenge hint says password was written under a "rock", which points directly to rockyou.txt. Username context in the challenge text gives abel as the credential spray target.
Spray and Pray - II
Pivot from the abel foothold (Part I) to niki and read local2.txt. Credentials are hidden inside a .docx in abel's Documents.
Spray and Pray - III
Escalate to root on the same box as Parts I/II. niki has NOPASSWD sudo on a writable user-creation script that adds users to the sudo group.
Logon Test
Platform sanity check. The flag is printed in the challenge description; submit it for a free point.
Routine - I
Target runs Grafana 8.3.0 + SSH. Path: Grafana path-traversal (CVE-2021-43798) -> dump grafana.db -> extract creds -> SSH for the user flag.
Routine - II
From the Routine-I foothold (tellytubby), escalate to root. A root cron runs /opt/backup.sh, which executes a tellytubby-writable Python file -> code injection as root.
Chain of Attacks - I
Target exposes IMAP (143), HTTP RiteCMS (8080), and Webmin (9090). Attack path for Part I
Chain of Attacks - II
Continue from the Part I www-data webshell. Escalate to root and read /root/proof.txt
Chain of Attacks - III BONUS: The VMDK Ghost Flag
I want to be fully transparent. The official rules state that mounting, modifying, or directly accessing the VM disk / box files outside the challenge environment is not an intended method.
The Art of Evasion & Persistence - I
Windows box exposing FTP and SMB. The path
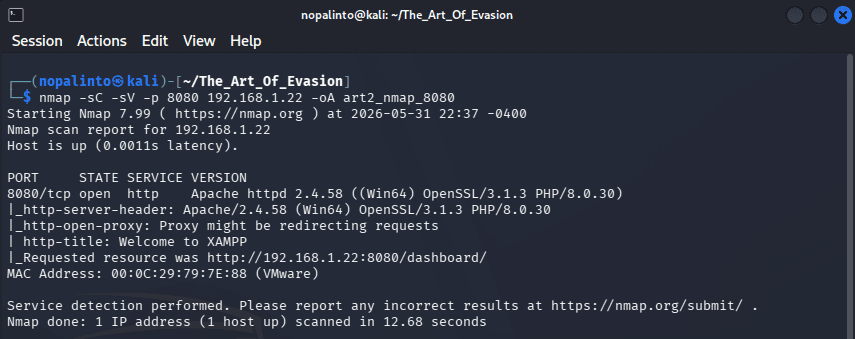
The Art of Evasion & Persistence - II
Reuse the Part I creds (webadmin:webhead2290) on RiteCMS (8080). PHP execution in media/ is blocked by .htaccess; delete it via the file manager, upload a PHP payload, and read C:\Users\Administrator\Desktop\proof.txt as nt authority\system.
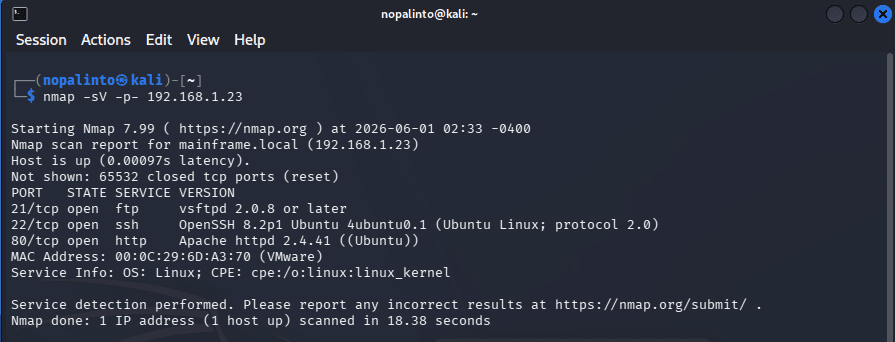
Rebornet
Rebornet is a Boot2Root machine exposing three services: anonymous FTP (vsftpd), SSH (OpenSSH 8.2p1), and HTTP (Apache 2.4.41). The objective is to obtain a root shell and read the flag in OWASPKL{} format.
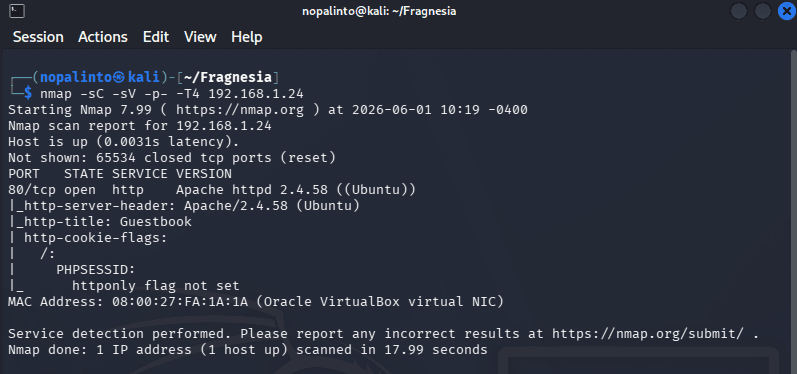
Fragnesia - I
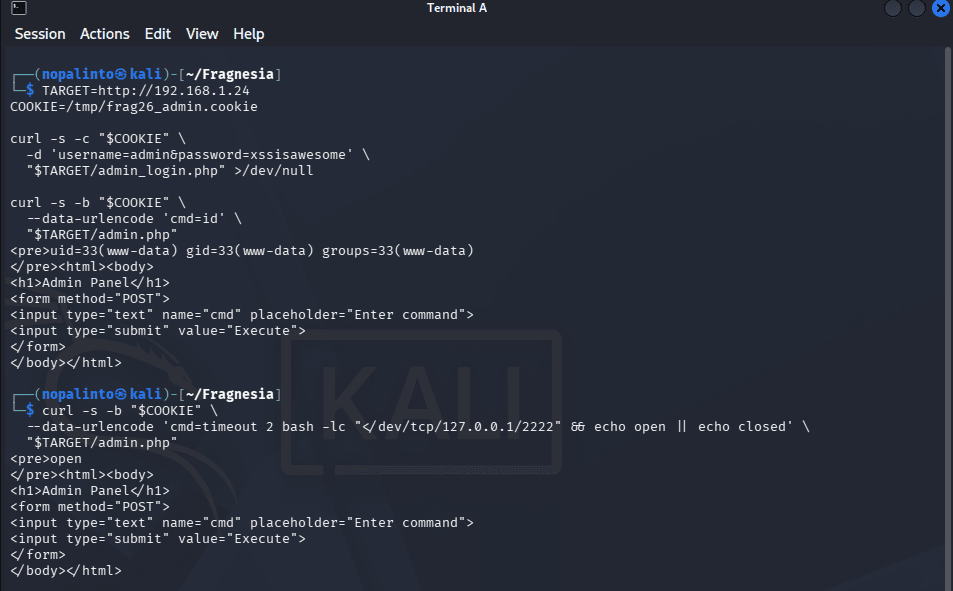
The challenge prompt "Can you command your orchestration without ever crossing the bounded rules?" points at driving a privileged internal action while staying inside the browser's Same-Origin Policy (the "bounded rules"). The target hosts a "Guestbook" web application. The intended path is a stored Cross-Site Scripting (XSS) flaw in the public guestbook that is rendered by an authenticated admin review bot. By making the bot execute our JavaScript in its own session, we hijack its admin context and reach a hidden command-execution panel, achieving Remote Code Execution (RCE) and reading the flag without ever submitting a password ourselves.
Fragnesia - II
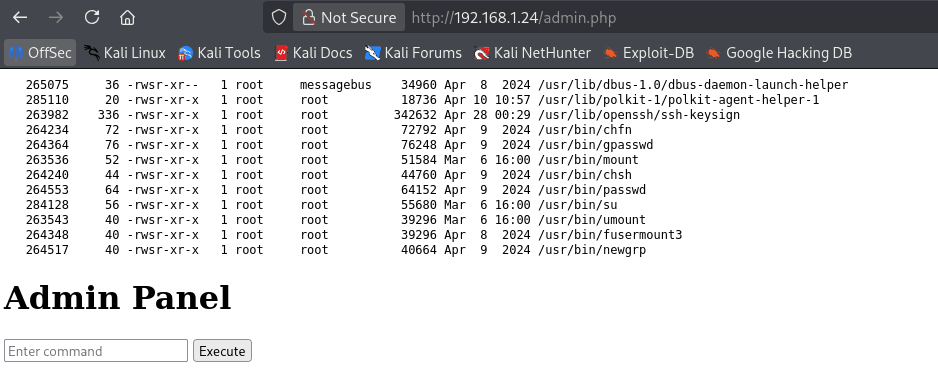
After completing Fragnesia - I, the stored XSS chain gave an authenticated admin session and command execution through admin.php. This stage focuses on using that www-data foothold to enumerate the host from the inside and pivot into the internal container that is not exposed directly on the network.
Fragnesia - III
After Fragnesia - II, I had already used the web RCE to pivot into an internal SSH container as the low-privileged user account and recover the second flag. The next step was to find the final flag.
Hakari Domain
MT19937 recovery into repeated RSA samples and Håstad broadcast recovery.
baby crypto
Hex stream reconstruction and ordered pair mapping from the encrypted output.
Hakari Domain 2
Remote crypto service analysis and scripted recovery for the second Hakari challenge.
Meowww
Stego and PowerShell payload recovery from a suspicious image artifact.
Dear Hiring Manger
Malicious PDF object analysis and ASCII85 payload reconstruction.
detonator
Executable triage with strings, object analysis, and scripted flag recovery.
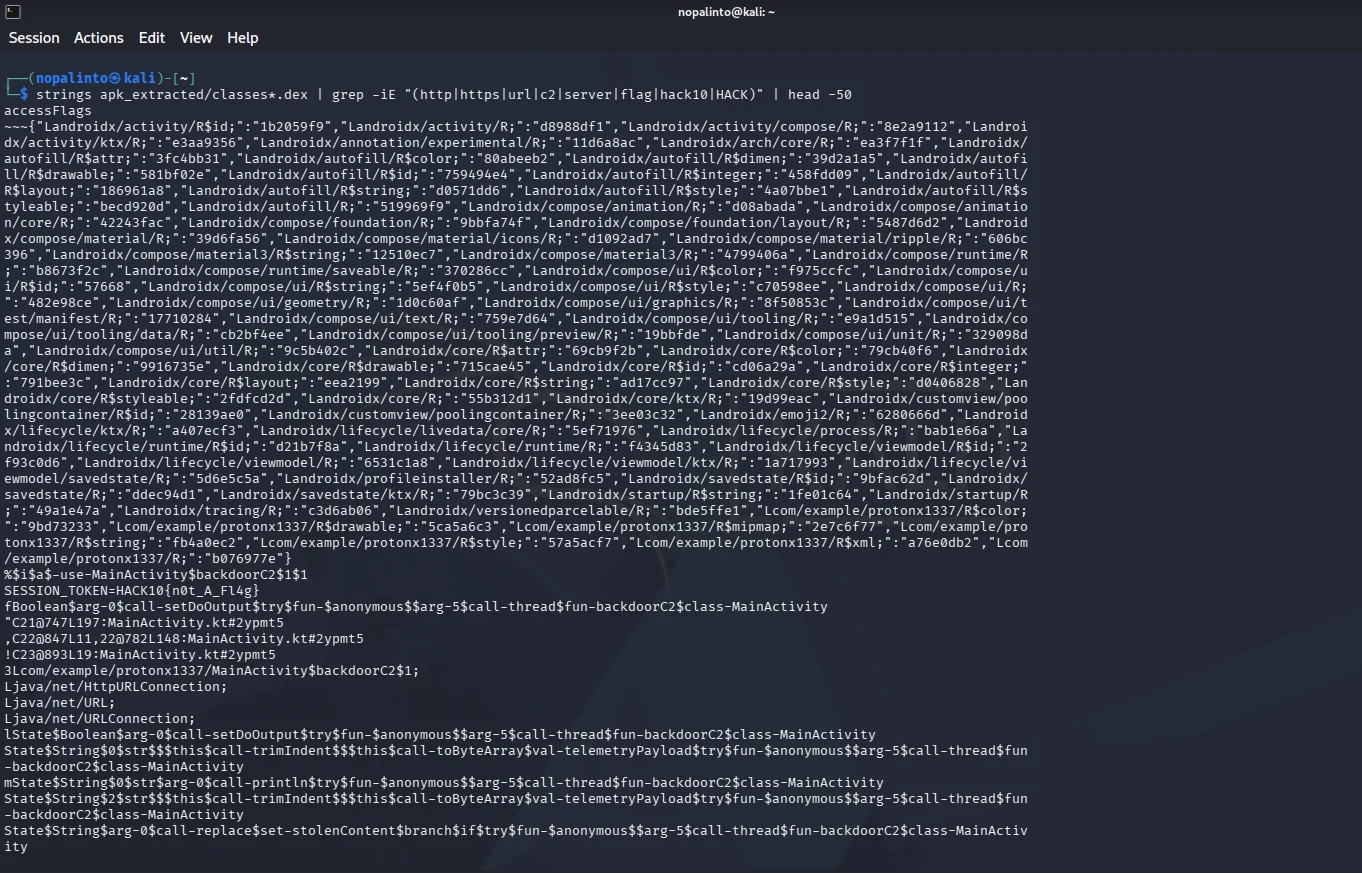
Proton X1337
APK decompilation, hidden C2 reconstruction, and server-side flag retrieval.
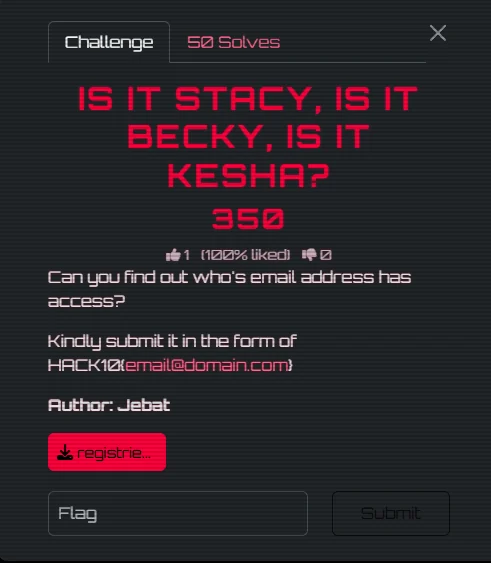
is it stacy, is it becky, is it kesha?
Registry and binary artifact reversal to recover the expected email-format flag.
easy re
APK and binary resource inspection using jadx, apktool, and Python helpers.
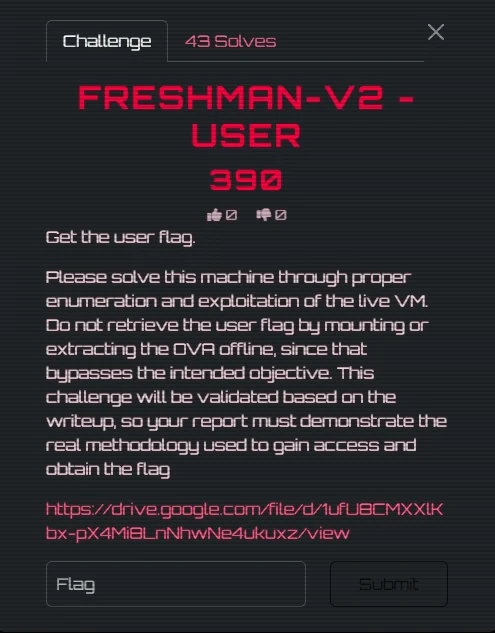
Freshman-V2 - user
Initial access path for the Freshman-V2 target.
Freshman-V2 - root
Privilege escalation path from user access to root on Freshman-V2.
Library-V2 - user
Anonymous FTP to SSH workflow for the Library-V2 user flag.
Library-V2 - root
Cron and tar wildcard privilege escalation for the Library-V2 root flag.
Phantom Relay
HTTP workflow abuse and scripted relay escape.
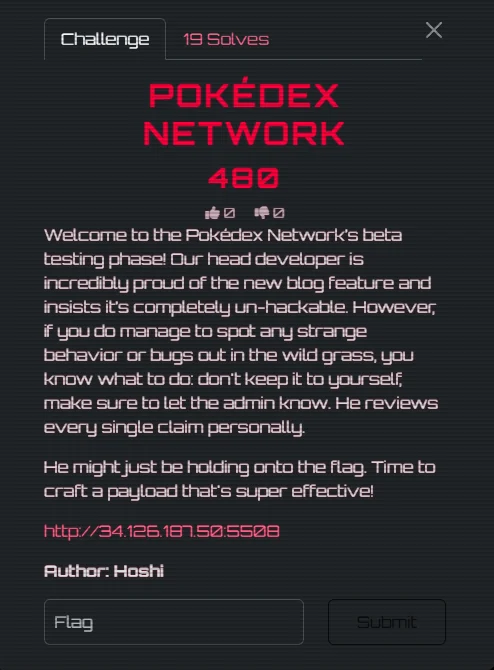
Pokedex Network
Endpoint discovery, XSS reasoning, and webhook-driven proof collection.
iCTFF8 Grand Final
Grand final recap from UiTM Melaka Jasin with the full PDF writeup attached.